To open a port in Windows 10, create an inbound rule in Windows Defender Firewall with Advanced Security. Select Inbound Rules > New Rule, choose Port, pick TCP or UDP, enter the port number, and select Allow the connection. Then choose the network types and give the rule a name.
Applies to: Windows 10. Windows 10 reached end of support on October 14, 2025, and only PCs enrolled in Extended Security Updates still get security fixes, through October 12, 2027.
You need an administrator account. Only open the ports an app or game tells you it needs, and remove the rule when you no longer use it. If you change the Remote Desktop (RDP) port, open the new port here.
What opening a port does
A port is a numbered doorway that network traffic uses to reach a specific program on your PC. Windows Defender Firewall blocks unsolicited incoming traffic by default, so a server, game host, or remote-access tool can’t accept connections until you allow its port. Some ports you may be asked to open:
- 3389 (TCP): Remote Desktop.
- 80 and 443 (TCP): a web server you run on the PC. Windows has a web server of its own, which you can turn on with IIS in Windows 10.
- 22 (TCP): an SSH server.
- 25565 (TCP): a Minecraft Java Edition server.
Avoid opening file-sharing ports such as 445 to the internet. Use the exact port and protocol the app’s documentation lists.
TCP or UDP?
The app or game’s documentation tells you which protocol to open. Web servers and Remote Desktop use TCP. Many games and voice apps use UDP, and some need both. If it lists both, create two rules with the same port number, one for each protocol. FTP also uses TCP, on port 21 plus a range of passive data ports, as explained in how to enable FTP in Windows 10. For example, after you set up the Apache web server on Windows 10, an inbound TCP rule for port 80 lets other devices on your home network open its pages. Database servers are a common case: a default SQL Server instance listens on TCP port 1433, and setting up SQL Server on Windows 10 explains when remote access is worth enabling.
Create an inbound rule
- Select Start, type Windows Defender Firewall with Advanced Security, and open it. You can also press Windows + R, type wf.msc, and press Enter.
- Select Inbound Rules on the left, then New Rule on the right.
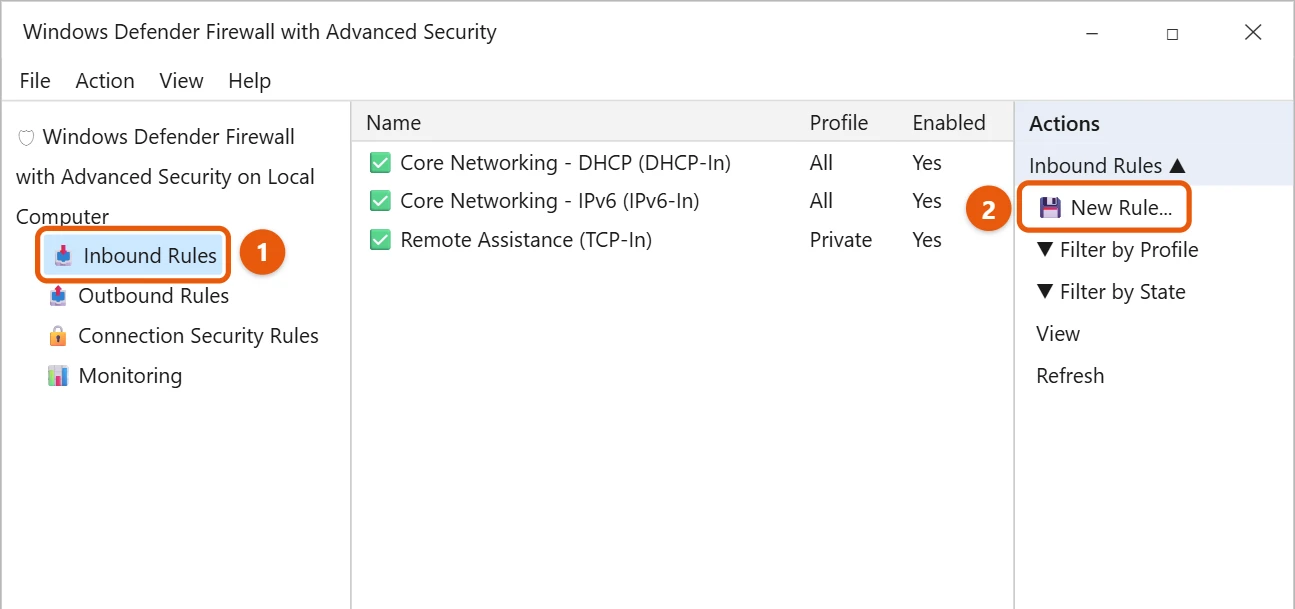
- Choose Port and select Next.
- Choose TCP or UDP, select Specific local ports, and type the port, such as 8080. You can list several ports with commas, or a range with a dash.
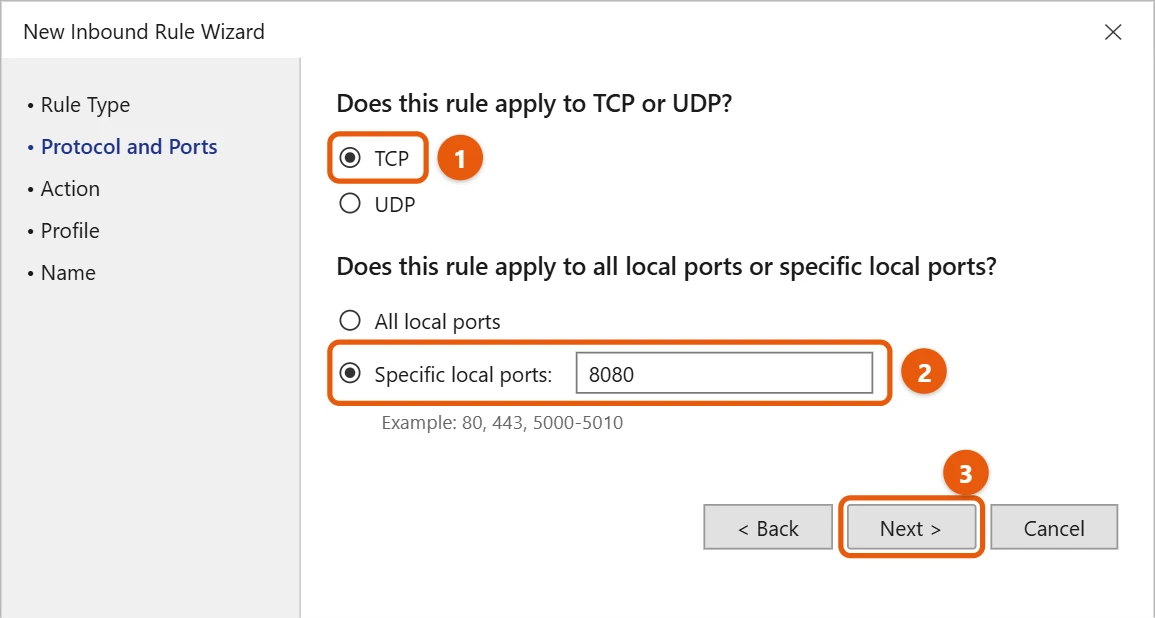
- Choose Allow the connection and select Next.
- Choose where the rule applies. Leave Private checked for your home network, and clear Public unless you really need it.
- Type a name you’ll recognize, such as Contoso app 8080, and select Finish.
If the app needs both TCP and UDP, make a second rule for the other one.
Open a port with PowerShell
Open PowerShell as an administrator and run a command like this one, changing the name and port:
New-NetFirewallRule -DisplayName "Contoso app 8080" -Direction Inbound -Protocol TCP -LocalPort 8080 -Action Allow -Profile Private
Check that it worked
- Make sure the app is running. A port only accepts connections when a program is listening on it, which you can confirm by finding port numbers in Windows 10.
- If other PCs on your network still can’t connect, check that your network is set to Private in Settings > Network & Internet.
- For access from outside your home, you also need to set up port forwarding on your router. Check your router’s instructions. If a game is the reason you are opening ports, check your NAT type first to see whether the router is the limit.
Test the port from another PC
On another Windows PC on the same network, open PowerShell and run, using your PC’s name or IP address and the port:
Test-NetConnection -ComputerName 192.168.1.20 -Port 3389TcpTestSucceeded : True means the port is open and something is listening. This test only works for TCP ports.
More rule options
- Use Command Prompt instead of PowerShell. In an administrator Command Prompt, run
netsh advfirewall firewall add rule name="Contoso app 8080" dir=in action=allow protocol=TCP localport=8080. - Only allow certain computers. Right-click your rule, select Properties, open the Scope tab, and under Remote IP address choose These IP addresses. Add the addresses that should be allowed in, such as one other PC on your network.
- Open an outbound port. If your network blocks outgoing traffic, or a security tool asks for it, repeat the same steps under Outbound Rules instead of Inbound Rules.
- Find your rule later. In Inbound Rules, select Filter by State > Filter by Enabled, or sort by Name, to see the rules you added.
If the port still looks closed
- Another firewall is in charge. Antivirus suites such as Norton or McAfee often replace Windows Defender Firewall. Open the port in that program instead.
- The rule is on the wrong profile. Open the rule’s Advanced tab and make sure the network type you’re on (Private, Public, or Domain) is checked.
- The app only listens on its own PC. Some apps listen on localhost (127.0.0.1) by default. Check the app’s settings for an option to allow network or remote connections.
- It works at home but not from the internet. Besides port forwarding, some internet providers share one public address among many customers, which blocks incoming connections. Ask your provider whether you have a public IP address.
Close the port again
Open Inbound Rules, right-click your rule, and select Disable Rule or Delete.
Frequently asked questions
Should I turn off the firewall instead?
No. Opening one port is much safer than turning the firewall off. If you do turn off the firewall in Windows 10 while troubleshooting, turn it back on when you’re done.
Do I need an outbound rule too?
Usually not. Windows Firewall allows outbound connections by default, so you only need an inbound rule.
How do I let an app through without picking a port?
In Windows Defender Firewall, select Allow an app or feature through Windows Defender Firewall and check the app.
Rule settings are documented in Microsoft’s Windows Firewall rules and New-NetFirewallRule.
On a Windows 11 PC, follow opening ports on Windows 11 instead.

Matt Jacobs writes and maintains the guides on Support Your Tech, which he started in 2017. He spent most of his career keeping small-business PCs running and still takes the occasional consulting job, so the steps here come from fixing the same problems on other people’s computers. Every guide is checked on his own Windows 11, Windows 10, Mac, iPhone and iPad before it goes up.