To check event logs in Windows 11, right-click Start and select Event Viewer. In the left pane, expand Windows Logs and select System or Application. The newest events are at the top. Select any event to see its details in the lower pane.
Event logs are most useful when you’re chasing a specific problem, such as a crash, a restart, or an app that won’t open. Most entries are routine, so the steps below show how to find the ones that matter.
Applies to: Windows 11. Checked against Microsoft documentation on October 10, 2026.
Open Event Viewer
Use any of these:
- Right-click Start (or press Windows + X) and select Event Viewer.
- Select Start or the search box, type
Event Viewer, and open it from the results. - Press Windows + R, type
eventvwr.msc, and press Enter.
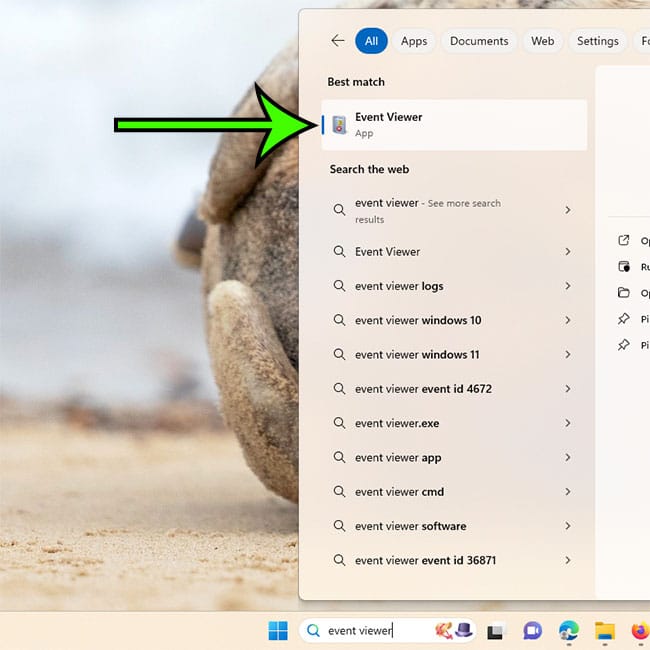
You can also reach it through Computer Management: right-click Start, select Computer Management, and expand System Tools > Event Viewer.
Event Viewer opens on Overview and Summary. The Summary of Administrative Events box counts Critical, Error, Warning, and Information events for the last hour, 24 hours, and 7 days. Expand a level to see which sources logged them, and double-click a source to list those events. It’s a quick way to spot a burst of errors before you open a specific log.
Find the log you need
- In the left pane, expand Windows Logs.
- Select System, Application, or Security.
- Select an event in the middle pane. The General tab below it explains what happened.
- System: Windows itself, drivers, and hardware. Start here for crashes, restarts, and device problems. If the errors point to a failing part, run hardware diagnostics next.
- Application: errors from programs such as Office or your browser.
- Security: sign-ins and other security events. You need to be an administrator to see it. Event logs are only one of the places to view activity history on Windows 11.
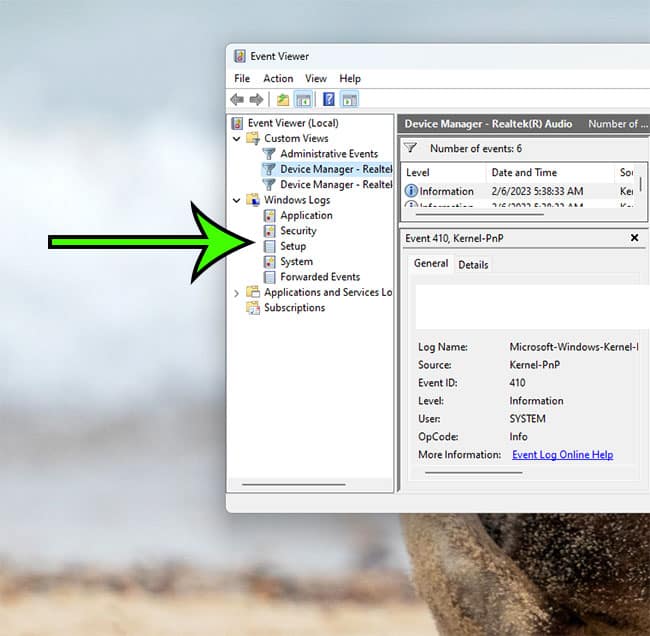
For a quick list of every error and warning across all logs, expand Custom Views and select Administrative Events.
The other logs are less useful day to day. Setup records Windows updates and feature installs. Forwarded Events stays empty unless the PC is set up to collect events from other computers, which is mostly done in offices.
Below Windows Logs, Applications and Services Logs holds separate logs for individual parts of Windows. Expand Microsoft > Windows, then open a component and select Operational. These are worth knowing:
- WindowsUpdateClient > Operational: update downloads, installs, and failures, with error codes.
- Windows Defender > Operational: threats Microsoft Defender Antivirus found and what it did with them.
- TaskScheduler > Operational: when scheduled tasks ran. If it’s empty, history is turned off; in Task Scheduler, select Enable All Tasks History in the Actions pane.
Show only errors
Logs hold thousands of entries. To see only the problems:
- Select the log, such as System.
- In the Actions pane on the right, select Filter Current Log.
- Under Event level, check Critical and Error. Set Logged to a time range, such as Last 24 hours.
- Select OK.
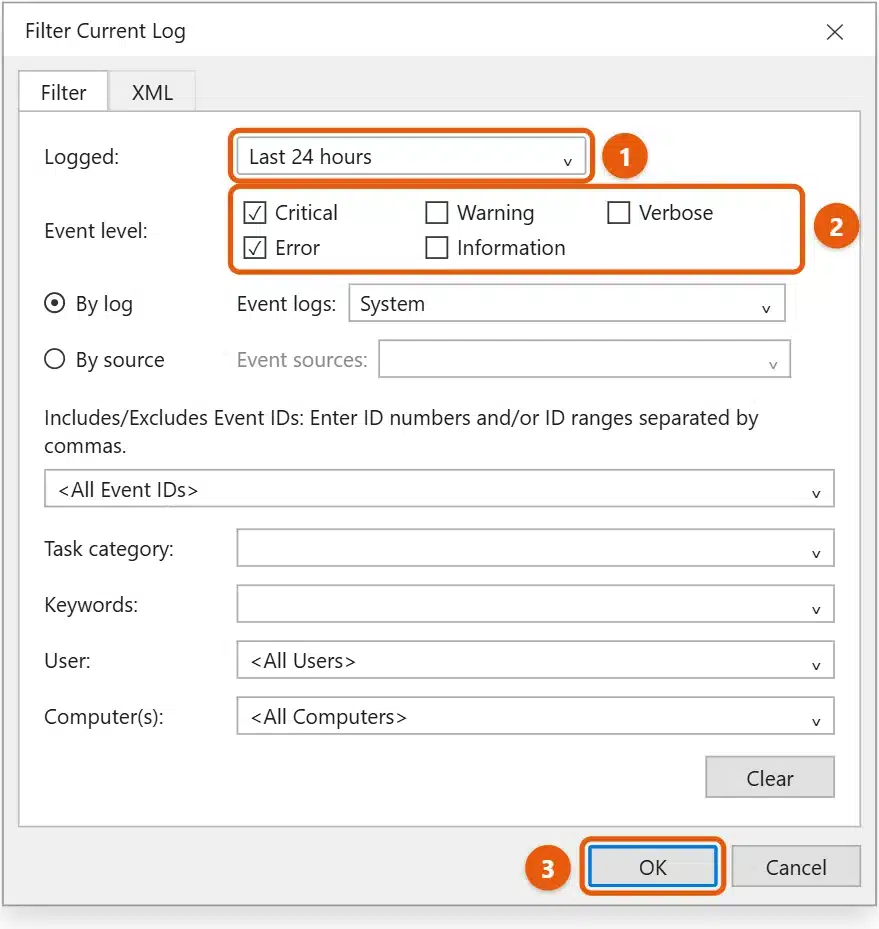
To see everything again, select Clear Filter in the Actions pane. To find a specific event, select Find in the Actions pane and type a word or event ID.
Search with Find, or save a filter as a custom view
Filter Current Log hides everything that doesn’t match. Find works differently: it jumps to the next event containing your word or number while still showing the rest of the log, so you can see what happened just before and after it.
- Select the log, then select Find in the Actions pane.
- Type a word, source, or event ID, such as Kernel-Power, and select Find Next.
- Select Find Next again to move to the next match.
If you check the same events often, save the filter so you don’t have to rebuild it:
- Select Create Custom View in the Actions pane.
- Choose a time range under Logged and check the event levels you want, such as Critical and Error.
- Choose By log and tick the logs to include, such as System and Application. You can also enter event IDs, separated by commas.
- Select OK, give the view a name such as Recent problems, and select OK again.
The view appears under Custom Views and updates every time you open it. Unlike a filter, it can combine several logs into one list.
Understand what you’re seeing
Each event has a level:
- Critical: a serious failure, such as Windows restarting without shutting down properly.
- Error: something failed, such as a driver or app not starting.
- Warning: something may cause a problem later. Many warnings are harmless.
- Information: normal activity. You can usually ignore these.
In the lower pane, note the Source (the part of Windows or the app that logged it), the Event ID, and the Logged time. Occasional errors are normal on a working PC. Look for an error that repeats, or one logged at the same time as your problem, and search for its source and event ID together to find the fix.
A fifth level, Verbose, holds detailed diagnostic messages. You’ll mostly see it in the logs under Applications and Services Logs.
The General tab gives the plain description. The Details tab shows the same event as raw data, in Friendly View or XML View; some events, such as event ID 41, include extra values there, like the BugcheckCode. Double-click an event to open it in its own window, where Copy copies everything as text you can paste into an email or support chat.
Common events to look for
- Kernel-Power, event ID 41 (System log, Critical): Windows restarted without shutting down cleanly. This follows a blue screen crash, a power cut, a drained battery, or holding down the power button.
- EventLog, event ID 6008 (System log): the previous shutdown was unexpected, logged with the time it happened.
- Application Error, event ID 1000 (Application log): an app crashed. The details name the app and the file that failed.
- BugCheck, event ID 1001 (System log): Windows recovered from a blue screen. The details include the stop code.
These IDs also come up often:
- User32, event ID 1074 (System): a program or person restarted or shut down the PC. The details name the process and user, which shows whether Windows Update restarted it.
- EventLog, event IDs 6005 and 6006 (System): the event log service started (the PC booted) and stopped (a clean shutdown). A 6005 with no 6006 before it points to a crash or power loss.
- Service Control Manager, event IDs 7000 and 7034 (System): a service didn’t start, or stopped unexpectedly. The details name the service.
- DistributedCOM, event ID 10016 (System): a permissions warning that appears on almost every PC. You can ignore it.
- Disk, event IDs 7, 51, and 153 (System): problems reading from or writing to a drive. If these repeat, back up your files and check the drive.
- Event IDs 4624 and 4625 (Security): a successful and a failed sign-in, if the PC is set to audit sign-ins.
Example: find out why your PC restarted
This puts the steps above together for the most common question people bring to Event Viewer.
- Note roughly when the restart happened.
- Open Event Viewer, expand Windows Logs, and select System.
- Select Filter Current Log, set Logged to Last 24 hours (or a custom range around the restart), and select OK.
- Look for event ID 1074 near that time. If it’s there, the restart was requested, and the details say by what, such as an update or a user.
- If there’s no 1074, look for Kernel-Power event ID 41 and EventLog event ID 6008. Together they mean Windows stopped without shutting down: a crash, a power cut, or a held power button.
- Check the events logged just before the 41. A disk error, a stopped service, or a BugCheck 1001 entry with a stop code usually points to the cause.
If restarts keep happening with no clear cause in the log, Reliability Monitor (below) often makes the pattern easier to see.
Use Reliability Monitor for a simpler view
Reliability Monitor shows crashes and failures on a timeline, one day per column, which is often easier than reading raw logs.
- Select Start, type
reliability, and open View reliability history. - Select a day with a red X to see what failed.
- Select View technical details on any entry for more information.
If a support person asks for your logs, select the log in Event Viewer, then select Save All Events As (or Save Filtered Log File As) in the Actions pane. Save it as an .evtx file.
Avoid Clear Log unless you’re told to use it. Cleared events can’t be recovered.
Other options in the Actions pane:
- Save Selected Events: select one or more events first (hold Ctrl to pick several), and save just those.
- Save All Events in Custom View As: saves the events a custom view shows.
- Clear Log > Save and Clear: saves a copy before emptying the log, if you’ve been asked to clear it.
Windows keeps the log files themselves in C:\Windows\System32\winevt\Logs, one .evtx file per log. Saving from Event Viewer is easier than copying those files, which are in use while Windows runs.
If Event Viewer won’t open or shows nothing
Most Event Viewer problems come from permissions, a stopped service, or a filter you forgot about. Try these fixes in order.
You get an “access denied” message on the Security log
The Security log needs administrator rights. Close Event Viewer, search for Event Viewer in Start, and select Run as administrator. If you’re on a standard account, sign in with an administrator account or ask the person who manages the PC.
A log is empty or stops at an old date
First check for a leftover filter. If the middle pane says Filtered at the top, select Clear Filter in the Actions pane. If there’s no filter, the Windows Event Log service may not be running:
- Press Windows + R, type
services.msc, and press Enter. - Double-click Windows Event Log.
- Set Startup type to Automatic, select Start if it’s stopped, and select OK.
Some logs under Applications and Services Logs are turned off by default. Right-click the log and choose Enable Log. It only records events from that point on.
Old events keep disappearing
Each log has a size limit, and Windows overwrites the oldest events when it’s full. Right-click the log, select Properties, and raise Maximum log size (KB). If you need to keep a record of a problem, use Save All Events As before it’s overwritten.
Event Viewer is slow or stops responding
Large logs take a while to load, especially Security on a busy PC. Wait for the progress bar in the middle pane to finish, then filter the log or open a custom view so it only loads the events you need. Closing other open logs also helps.
Event Viewer shows an MMC or snap-in error
An error such as “MMC could not create the snap-in” usually means damaged system files. Open Terminal as administrator and run these two commands, then restart:
sfc /scannow
DISM /Online /Cleanup-Image /RestoreHealth
Frequently asked questions
Do errors in Event Viewer mean something is wrong with my PC?
Not usually. Every Windows PC logs errors and warnings during normal use. Only look into errors that line up with a problem you’ve noticed.
Is it safe to use Event Viewer?
Yes. Viewing and filtering logs doesn’t change anything on your PC. Be wary of phone calls or pop-ups that show you Event Viewer errors to convince you your PC is infected. That’s a common scam.
Can I see event logs from the command line?
Yes. In Terminal, Get-WinEvent -LogName System -MaxEvents 20 shows the 20 most recent System events. To list only errors and critical events from the last day, run Get-WinEvent -FilterHashtable @{LogName='System'; Level=1,2; StartTime=(Get-Date).AddDays(-1)}. In Command Prompt, wevtutil qe System /c:10 /rd:true /f:text prints the 10 newest System events. Microsoft’s Get-WinEvent reference lists more filters. Older guides use Get-EventLog, which isn’t available in PowerShell 7.
How long does Windows keep event logs?
There’s no fixed number of days. Each log keeps events until it reaches its maximum size, then the oldest entries are overwritten. On a busy PC that can be a few days for the System log, and much longer on a quiet one. Raising the maximum size in the log’s Properties keeps more history.
Using Windows 10? See how to check event logs in Windows 10. Microsoft explains event ID 41 in Advanced troubleshooting for Event ID 41. More help is on our Windows 11 Help & Guides page.
To keep a copy of an error message, see how to take a screenshot in Windows 11.
For other built-in tools that help with problems, see how to open Command Prompt in Windows 11.
Related: How to check computer activity history on Windows 10.
Related: How to Check Print History in Windows 11.
Matt Jacobs has been working as an IT consultant for small businesses since receiving his Master’s degree in 2003. While he still does some consulting work, his primary focus now is on creating technology support content for SupportYourTech.com.
His work can be found on many websites and focuses on topics such as Microsoft Office, Apple devices, Android devices, Photoshop, and more.