Last updated on November 10th, 2026 at 10:15 am
Secure Boot is turned on in PC firmware, not inside Windows 11. Check that msinfo32 shows BIOS Mode: UEFI; Legacy means converting the drive to GPT. Open Settings > System > Recovery, select Restart now by Advanced startup, and choose Troubleshoot > Advanced options > UEFI Firmware Settings > Restart. Set Secure Boot to Enabled and save with F10. Labels vary by maker; Microsoft’s Windows 11 and Secure Boot page covers the Windows side.
What Secure Boot does, and why Windows 11 cares
Secure Boot is a setting in your PC’s firmware (the UEFI, often still called the BIOS) that runs before Windows. It only lets startup software with a trusted digital signature load, which blocks bootkits and other malware that tries to start before Windows and your antivirus do.
Microsoft’s Windows 11 specifications list the firmware requirement as “UEFI, Secure Boot capable.” So a PC can run Windows 11 with Secure Boot switched off, but Microsoft recommends turning it on. Two common reasons people go looking for this setting: PC Health Check or Windows 11 Setup says This PC must support Secure Boot, or a game’s anti-cheat software refuses to start without it.
Step 1: Check whether Secure Boot is already on
- Press Windows key + R, type
msinfo32, and press Enter. - With System Summary selected on the left, find BIOS Mode and Secure Boot State in the right pane. Press Ctrl + F and search for “secure boot” if the list is long.

| BIOS Mode | Secure Boot State | What it means |
|---|---|---|
| UEFI | On | You’re done. Secure Boot is already working. |
| UEFI | Off | The PC supports it; you just need to enable it. Go to Step 2. |
| Legacy | Unsupported | The PC is booting in old BIOS (CSM) mode. Convert the drive to GPT first. |
You can also open Windows Security > Device security. Since 2026, that page has a Secure Boot section that also reports whether your PC has received Microsoft’s newer Secure Boot certificates (more on that below).
Before you change firmware settings
- Have your BitLocker recovery key ready. If your drive is encrypted (BitLocker or Device encryption), firmware changes can make Windows ask for the 48-digit recovery key at the next start. If you aren’t sure where it is, find your BitLocker recovery key before you continue.
- Suspend BitLocker if you can. Microsoft recommends suspending protection before planned firmware changes. In Terminal (Admin), run
manage-bde -protectors -disable C: -rc 3. The drive stays encrypted, and protection turns back on by itself after three restarts. The manage-bde protectors reference explains the options. - Plug in your laptop. Don’t let it lose power while you’re in the firmware menu.
- Take a photo of each firmware screen before changing anything, so you can put settings back exactly as they were.
Step 2: Restart into the UEFI firmware settings
- Save your work and close your apps.
- Select Start > Settings > System > Recovery.
- Next to Advanced startup, select Restart now, then confirm. The PC restarts to a blue Choose an option screen.
- Select Troubleshoot > Advanced options > UEFI Firmware Settings, then Restart. Don’t pick Reset this PC, which reinstalls Windows.
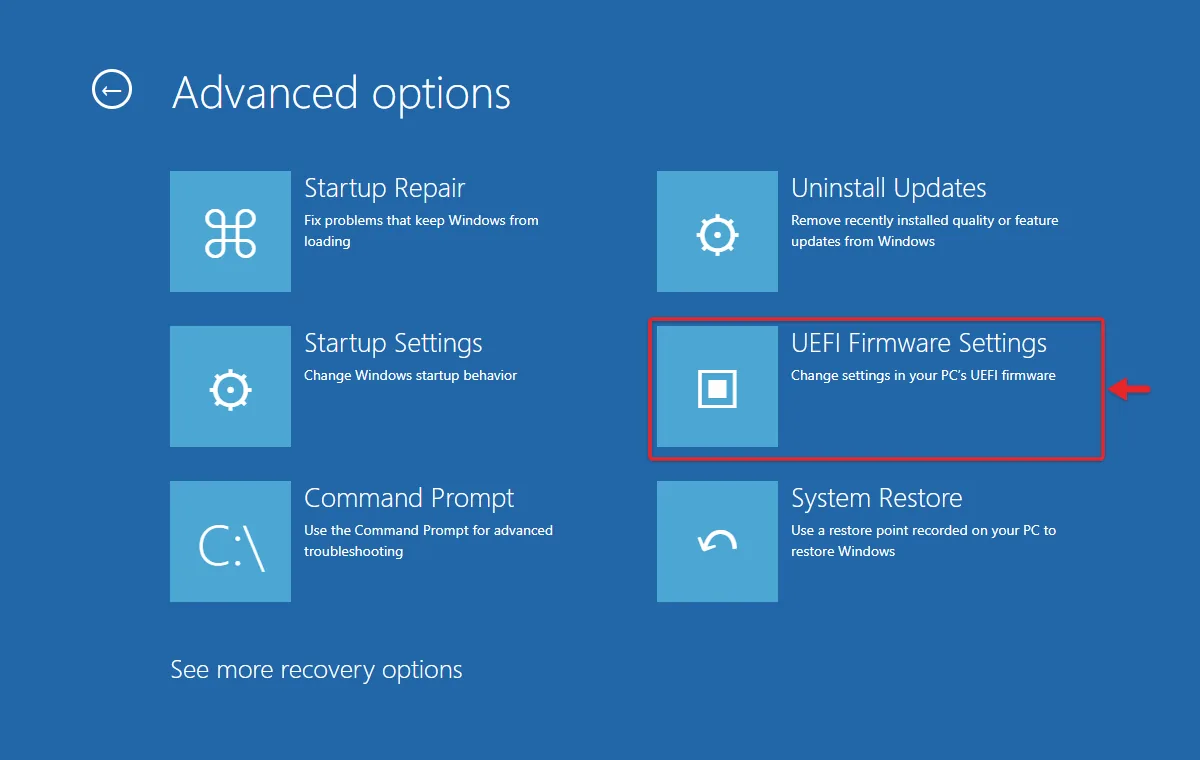
The PC restarts straight into its firmware setup screen. If you’d rather use a key at power-on, it’s usually F2 or Delete on most desktops and many laptops, F10 on HP, and F1 or F2 on Lenovo. There are more ways to enter BIOS (UEFI) in Windows 11 if neither route works. For ThinkPad, IdeaPad and other models, here is how to get into the BIOS on a Lenovo laptop or desktop, including the Novo button.
If UEFI Firmware Settings is missing from the Advanced options list, Windows was started in Legacy mode. Jump to If BIOS Mode says Legacy.
Step 3: Enable Secure Boot in the firmware
- If the firmware opens in a simplified screen, switch to the advanced view (often F7 on ASUS and MSI boards, F2 on Gigabyte boards).
- Open the tab that holds boot security. Depending on the maker it’s called Boot, Security, Authentication or System Configuration.
- If you see CSM (Compatibility Support Module), Legacy Support or a Boot Mode option, set it to Disabled or UEFI. Secure Boot stays greyed out while legacy booting is allowed. Only do this if msinfo32 showed BIOS Mode: UEFI.
- Set Secure Boot (sometimes Secure Boot Control) to Enabled. If there’s a Secure Boot Mode option, leave it on Standard. Custom mode is for people managing their own keys.
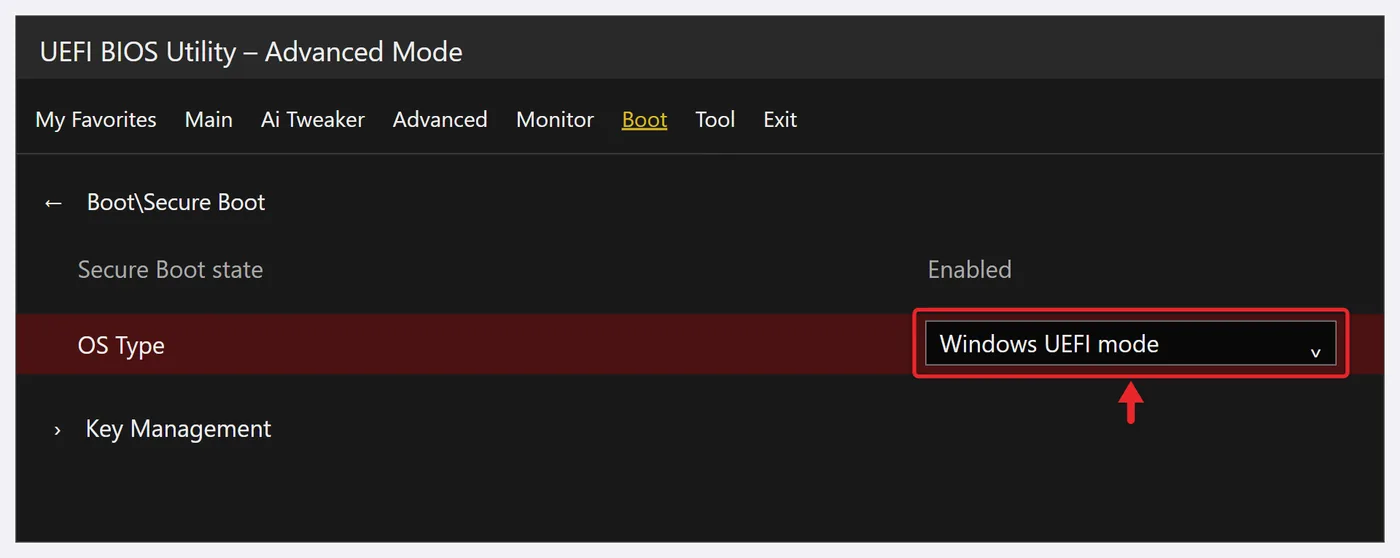
- If the screen shows a System Mode of Setup, or Secure Boot won’t stay enabled, choose Restore Factory Keys or Install default Secure Boot keys and confirm. This loads the standard keys that trust Windows.
- Press F10 (or go to Exit > Save Changes and Exit) and confirm. Pressing Esc on some firmware leaves without saving.
The PC restarts and Windows loads as usual. Nothing on your drive changes when you turn Secure Boot on.
Where the setting usually is, by maker
| PC or board | Usual location |
|---|---|
| Dell laptops and desktops | A Secure Boot section |
| HP | System Configuration or Security, then Secure Boot Configuration; turn off Legacy Support there too |
| Lenovo | Security > Secure Boot |
| ASUS boards | Advanced mode (F7), Boot > Secure Boot |
| Gigabyte boards | Boot tab: set CSM Support to Disabled, then open Secure Boot. Older boards may need Windows 8/10 Features set to the Windows (WHQL) option before Secure Boot appears |
If your menus look different, search your PC maker’s support site for your exact model. Microsoft’s Secure Boot page links to the support sites of several major manufacturers. If you have an MSI board, entering the BIOS on an MSI with Windows 11 shows where TPM and Secure Boot sit in Click BIOS.
Can I turn on Secure Boot without going into the BIOS?
No. Secure Boot is a firmware setting. Registry values and PowerShell commands only report its state or manage its key databases; they can’t switch it on. Advanced startup is the closest thing to a shortcut, because it opens the firmware without guessing a startup key.
Step 4: Confirm it worked
- Run
msinfo32again. Secure Boot State should now say On. - For a second check, open Terminal (Admin) and run
Confirm-SecureBootUEFI. It returns True when Secure Boot is on and False when it’s supported but off, per the Confirm-SecureBootUEFI reference.

- If you suspended BitLocker without a restart count, resume it with
manage-bde -protectors -enable C:. - If PC Health Check flagged Secure Boot earlier, open it and select Check now again.
To undo the change, go back into the firmware and set Secure Boot to Disabled. The full steps to turn off Secure Boot in Windows 11 cover that, including when it makes sense to leave it off.
If BIOS Mode says Legacy: convert the drive to GPT first
Secure Boot only works when Windows boots in UEFI mode, and UEFI boot needs a GPT drive. Windows includes the mbr2gpt tool to convert the system drive without reinstalling. Microsoft’s MBR2GPT documentation warns that the change can’t be undone, so back up your files first.
- Suspend BitLocker if the drive is encrypted (see above). MBR2GPT won’t convert a drive with active BitLocker protection.
- Right-click Start and select Terminal (Admin).
- Run
mbr2gpt /validate /allowFullOS. If it reports that validation completed successfully, continue. If it fails, the drive layout isn’t supported (for example, more than three primary partitions), and the tool stops without changing anything. - Run
mbr2gpt /convert /allowFullOSand wait for it to finish. - Restart into the firmware, change the boot mode from Legacy or CSM to UEFI, then enable Secure Boot as in Step 3 and save.
Don’t skip the last step: after conversion, the drive will only start in UEFI mode. If you switch to UEFI without converting the drive, Windows won’t start either; switch the setting back to Legacy to get in again.
Will turning on Secure Boot delete anything?
No. Enabling it doesn’t touch your files or apps. The only step with real risk is the MBR-to-GPT conversion for Legacy-mode PCs, which is why a backup comes first.
Secure Boot certificate updates in 2026
Microsoft’s original Secure Boot certificates from 2011 are being replaced. According to Microsoft’s page on Secure Boot certificate expiration and CA updates, two expired in June 2026 and the one that signs the Windows boot loader expired on October 19, 2026. PCs without the newer 2023 certificates keep starting and keep getting regular Windows updates, but they stop receiving new protections for the early boot process.
Most PCs get the new certificates automatically through Windows Update, sometimes with a firmware update from the PC maker. To check yours, open Windows Security > Device security > Secure Boot. Microsoft’s guide to Secure Boot certificate status in the Windows Security app explains each message. A yellow or red badge usually means you should install pending Windows updates, then check your PC maker’s site for a BIOS update. If you need one, see how to update your BIOS on Windows 11.
Secure Boot greyed out or still showing Off
The Secure Boot option is greyed out
Legacy booting is still allowed. Turn off CSM or Legacy Support, save, re-enter the firmware, and the option should unlock. On some business laptops, security settings stay locked until you set a supervisor (administrator) password in the firmware; set one, enable Secure Boot, and remove the password afterward if you don’t want it. An older board may also need a BIOS update before the option appears.
Secure Boot State still says Off
The change wasn’t saved, or the key database is empty. Go back in, choose Restore Factory Keys (or Install default Secure Boot keys), make sure Secure Boot is Enabled, and save with F10 rather than Esc.
The screen stays black or Windows won’t start
An old graphics card without UEFI support can give a blank screen once CSM is off, and a Legacy-mode Windows install won’t start in UEFI mode. Turn Secure Boot off and CSM back on (or load the firmware defaults) to get back in. If you can’t see the firmware screen, connect the monitor to the motherboard’s video output, or clear the CMOS following your board’s manual. Then convert the drive to GPT or update the graphics card before trying again.
Windows asks for a BitLocker recovery key
Type the key shown for your drive’s Key ID. Most personal PCs store it in the Microsoft account that set up the device. Windows then starts normally. Resume BitLocker afterward if you suspended it.
A game still says Secure Boot is required
Anti-cheat software such as Riot Vanguard (used by Valorant) can require Secure Boot and TPM 2.0 on Windows 11. Confirm Secure Boot State is On, then press Windows key + R, type tpm.msc, and check that the TPM is ready with Specification Version 2.0. If it isn’t, check and enable TPM in the firmware (the firmware steps are the same on Windows 11, where it’s often labeled Intel PTT or AMD fTPM). Restart once more so the anti-cheat service can load.
Does Secure Boot slow down my PC or block normal apps?
It only checks software that loads during startup, so everyday apps and games run the same. Startup time doesn’t change in any way you’d notice.
Will Linux still boot with Secure Boot on?
Many popular distributions ship signed boot loaders that work with Secure Boot, so a typical dual-boot setup keeps working. Distributions or custom kernels without signed boot components may refuse to start until you turn Secure Boot off or enroll your own keys.
I’m still on Windows 10. Are the steps different?
The firmware part is identical, but the Settings path to Advanced startup is different. Follow the steps to turn on Secure Boot in Windows 10 instead.
Once msinfo32 reports Secure Boot State: On, open Windows Security > Device security to make sure no certificate updates are waiting, and you’re finished.

Matt Jacobs writes and maintains the guides on Support Your Tech, which he started in 2017. He spent most of his career keeping small-business PCs running and still takes the occasional consulting job, so the steps here come from fixing the same problems on other people’s computers. Every guide is checked on his own Windows 11, Windows 10, Mac, iPhone and iPad before it goes up.