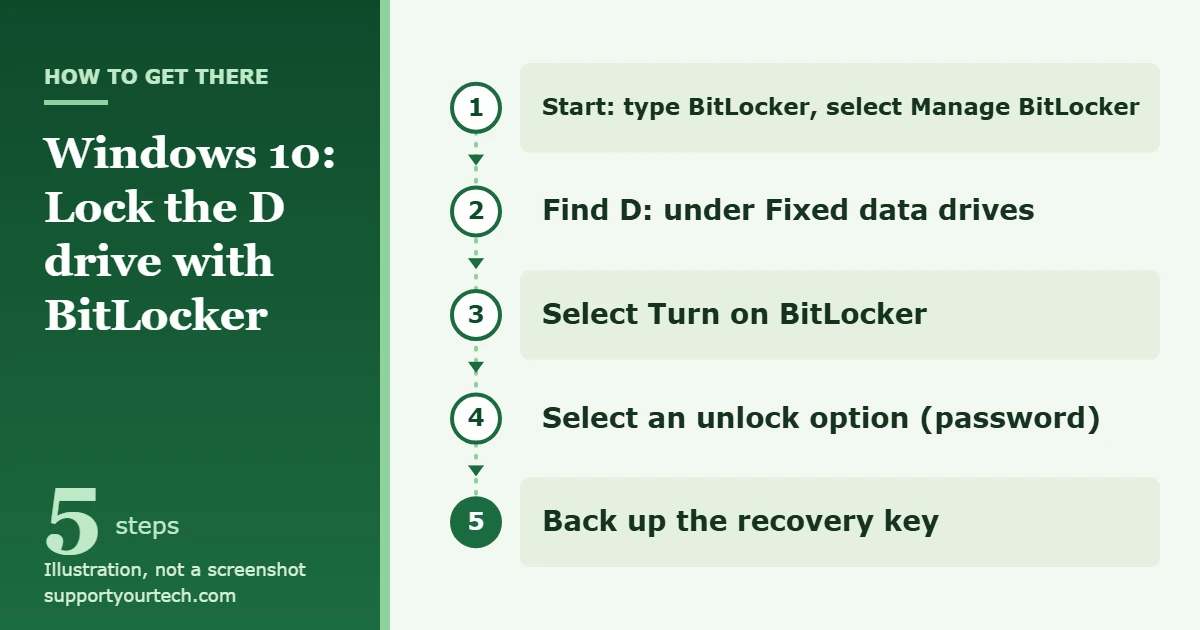
To lock the D drive in Windows 10, encrypt it with BitLocker: open Start, type BitLocker, select Manage BitLocker, find the D: drive under Fixed data drives, and select Turn on BitLocker. Choose a password as the unlock option, back up the recovery key, and let the encryption finish. After that, nobody can read the drive without the password or the recovery key, even if the drive is moved to another computer.
Applies to: Windows 10 Pro, Enterprise, and Education (the same BitLocker steps apply to Windows 11).
What “locking” a drive means in Windows 10
Windows 10 has no simple password switch for a drive. People who ask how to lock the D drive usually want one of three different things, and each has a different tool:
| Goal | Tool | What it really does |
|---|---|---|
| Nobody can read the files without a password | BitLocker Drive Encryption | Encrypts the whole drive. This is the only option here that protects the data if the drive or the PC is stolen. |
| Another person who uses the same PC should not open the drive | Separate Windows accounts and drive permissions | Windows blocks that account while Windows is running. The data itself is not encrypted. |
| The drive should not show up in File Explorer | A Group Policy setting that hides drives | Removes the drive icon only. It does not stop other programs from reaching the drive. |
If your goal is real protection, use BitLocker. The rest of this guide covers BitLocker first, then explains where the other two approaches fit. For other drives, see how to lock a drive in Windows 10.
Before you start
- Check your edition. BitLocker Drive Encryption is only available on Windows Pro, Enterprise, and Education. It is not in Windows 10 Home. If you are not sure which one you have, check which version of Windows you have.
- Sign in as an administrator. The BitLocker setup needs an administrator account.
- Back up the files on D: first. BitLocker encrypts the drive with your files in place, but a backup protects you if the drive fails or you later lose both the password and the recovery key.
- Decide where the recovery key will live. The recovery key is a 48-digit number that unlocks the drive if you forget the password. Pick a place that is not the D drive itself and is not kept with the computer.
- Work or school PC? BitLocker is usually managed by the IT department on those devices, so the options you see may be limited or already set for you.
A Trusted Platform Module (TPM) chip is not what unlocks a data drive such as D:. Data drives can be unlocked with a password or a smart card, so the password route below works on its own.
Lock the D drive with BitLocker
- Sign in to Windows with an administrator account.
- Select Start, type BitLocker, and select Manage BitLocker from the list of results. The BitLocker Drive Encryption window opens in Control Panel. If Manage BitLocker is not in the results, your edition of Windows does not include it.
- Look at the list of drives. The drive with Windows on it appears under Operating system drive. A second internal drive or partition such as D: appears under Fixed data drives. USB drives appear under Removable data drives – BitLocker To Go.
- Next to the D: drive, select Turn on BitLocker. A setup wizard opens.
- Select an unlock option. For a home PC, choose the password option and enter a strong password twice. This is the password you will type whenever the drive needs to be unlocked.
- Back up the recovery key when the wizard asks. You can save it to your Microsoft account, save it to a USB flash drive, save it to a file, or print it.
- Answer the remaining questions in the wizard, including how much of the drive to encrypt (see the next section), and start the encryption. This can take some time, and you can keep using the PC while it runs.
When encryption finishes, the D drive is protected. Files you open are decrypted only as they are read, and anything you save is encrypted before it is written, so you keep working with the drive the normal way once it is unlocked.
Used space only or the entire drive?
BitLocker can encrypt only the part of the drive that currently holds data, or the whole drive including empty space. Here is the trade-off:
- Used space only is much faster, especially on a new or nearly empty drive. New files are encrypted automatically as they are saved. It is not the most secure choice, because the free space on the drive is not encrypted.
- The entire drive takes longer but also covers that empty space. Choose it for a drive that has been in use for a while and has held private files.
How long either choice takes depends on the type, size, and speed of the drive. If the PC is shut down or hibernates partway through, encryption resumes where it stopped the next time Windows starts.
Keep the recovery key safe
The recovery key is your only fallback. Microsoft support staff cannot retrieve, provide, or recreate a lost BitLocker recovery key, and BitLocker is designed so that the drive cannot be recovered without the required authentication. Lose the password and the key, and the files on D: are gone.
You can make extra copies at any time:
- Select Start, search for BitLocker, and select Manage BitLocker.
- Next to the D: drive, select Back up your recovery key.
- Choose where to back it up: your Microsoft account, a USB flash drive, a file, or a printout.
- Select Finish.
Keep more than one backup. Do not store the USB drive or the printout with the computer, and never save the key on the encrypted drive. A key saved to a Microsoft account can be looked up later at aka.ms/myrecoverykey from any device. On a work or school device the key may be stored with the organization account instead. The full list of options is on Microsoft’s page on backing up your BitLocker recovery key.
Lock and unlock the drive on demand
Turning on BitLocker does not mean the drive stays closed while you are signed in. Once you unlock D: with the password it remains open, so someone who sits down at your unlocked PC can browse it. To close the drive again without restarting, use the manage-bde command-line tool that comes with BitLocker:
- Close any files and programs that are using the D drive.
- Open a Command Prompt window with administrator rights.
- Type manage-bde -lock D: and press Enter. The drive is locked, and its contents cannot be read until it is unlocked again.
- To open it from the same window, type manage-bde -unlock D: -password, press Enter, and enter the password when prompted.
You can also unlock a data drive from the BitLocker Drive Encryption window in Control Panel by using the password. If you forgot the password, unlock with the recovery key instead: manage-bde -unlock D: -recoverypassword followed by the 48-digit key, typed exactly as shown with its dashes.
Windows can also unlock a fixed data drive automatically when you sign in. There is one condition: automatic unlocking for a fixed data drive requires the operating system drive (usually C:) to be protected by BitLocker as well. If C: is not encrypted, D: cannot be set to unlock on its own, and you enter the password after each restart. For a drive you want kept away from other people who use the PC, entering the password each time is the safer setting anyway.
Command-line alternative
If you prefer commands, or the wizard will not open, you can turn BitLocker on from an administrator Command Prompt. For a data drive with a password, use this form:
- Type manage-bde -on D: -pw and press Enter, then set the password when asked.
- Add -usedspaceonly to the command if you want only the used space encrypted. Without it, used and free space are both encrypted.
- Add -recoverypassword to the command so that a numerical recovery password is created, and write it down somewhere safe.
This method uses the same BitLocker feature as the wizard, so it has the same edition requirement.
Confirm it worked, or undo it
To check the drive, open an administrator Command Prompt and type manage-bde -status D:. The report lists the percentage encrypted, the encryption method, the protection status, the lock status, and the key protectors for the drive. In PowerShell, Get-BitLockerVolume D: shows similar details, including whether protection is on and whether the drive is locked or unlocked. The BitLocker Drive Encryption window also shows the current state next to each drive.
To remove the lock for good, the drive has to be decrypted. In the BitLocker Drive Encryption window, use the turn-off option next to D:, or run manage-bde -off D:, which decrypts the drive and removes all key protectors when it finishes. Your files stay in place. Every step of turning off BitLocker in Windows 10 is covered separately.
If you have Windows 10 Home
Windows 10 Home does not include BitLocker Drive Encryption, so Manage BitLocker will not appear. Some Home PCs support a related feature called Device Encryption, which turns on BitLocker encryption automatically for the operating system drive and fixed drives when you sign in with a Microsoft account. It is all or nothing: you cannot pick only D: or set a separate password for it, and it depends on hardware such as a TPM and Secure Boot. To check whether your PC has it, use Microsoft’s Device Encryption in Windows page.
If Device Encryption is not available either, the supported route to BitLocker is a PC running a Pro edition. Be cautious with small utilities that claim to “lock” a drive with a password; many only hide the drive or block it while Windows is running, which is not the same as encrypting it.
Blocking another user or hiding the drive
These two approaches are not encryption, but they are sometimes enough for a shared family PC.
Separate accounts and permissions
If everyone has their own Windows account and only you are an administrator, you can change the permissions on the D drive so that a specific standard account is denied access. Windows then refuses to open the drive for that person. Keep the limits in mind: any administrator can change the permissions back, and permissions mean nothing if the drive is removed and connected to another computer. Take care not to deny access to your own account or to the administrators group, or you may lock yourself out.
Hiding the drive with Group Policy
Windows includes a policy named Hide these specified drives in My Computer, found under User Configuration > Administrative Templates > Windows Components > File Explorer. Enabling it and choosing Restrict D drive only removes the D: icon from File Explorer and from the Open dialog box in programs. Choosing Do not restrict drives brings it back.
This policy has clear limits: it does not prevent users from reaching the drive through other programs, and it does not stop them from viewing the drive in Disk Management. Treat it as a way to reduce clutter or accidents, not as security. The setting is described in Microsoft’s Using Group Policy Objects to hide specified drives.
Troubleshooting
- Manage BitLocker does not appear in Start. This means the device does not have the correct Windows edition. BitLocker Drive Encryption needs Pro, Enterprise, or Education.
- The D drive is not listed. Check which heading it falls under. An internal drive or partition is listed under Fixed data drives, while a USB or other removable drive is listed under Removable data drives – BitLocker To Go.
- Options are missing or you are not allowed to change them. Make sure you are signed in with an administrator account. On a work or school device, encryption is typically controlled by organizational policy, so contact your IT department.
- You forgot the password. Unlock with the 48-digit recovery key. Look in your Microsoft account at aka.ms/myrecoverykey, on the USB drive or text file where you saved it, or among your printed papers. For a work or school device, ask the IT department.
- You cannot find the recovery key anywhere. Microsoft cannot recreate it. Without the password or the key, the data on the drive cannot be recovered.
- The PC lost power during encryption. BitLocker resumes where it stopped the next time Windows starts, even after a sudden power loss.
Frequently asked questions
Can I put a password on the D drive without BitLocker?
Windows 10 has no other built-in feature that password-protects a whole drive. Permissions and hidden drives limit access inside Windows but do not encrypt anything. For a password that actually protects the data, BitLocker is the built-in answer.
Does the D drive lock again when I restart the PC?
Yes, unless automatic unlocking is set up. After a restart the drive stays locked until it is unlocked with the password. Automatic unlocking of a fixed data drive is only possible when the Windows drive is also protected by BitLocker.
Will BitLocker slow down my computer?
The cost is a small performance overhead, often in single-digit percentages of storage speed. BitLocker does not decrypt the whole drive when you use it; it works only on the data being read or written.
Will turning on BitLocker delete my files?
No. The files on the drive are encrypted in place and remain available while encryption runs in the background. A backup is still wise before any change that affects a whole drive.
Can I open the locked drive on another computer?
Yes. A BitLocker data drive can be unlocked on another computer from the BitLocker Drive Encryption item in Control Panel by using its password. That is also why the password and recovery key matter: without them, the drive stays unreadable on any PC.
Is it still worth doing this on Windows 10?
BitLocker continues to work, but Windows 10 reached the end of support on October 14, 2025, and Microsoft’s regular monthly security updates ran through that date. Encryption protects files on a lost or stolen drive; it does not protect an out-of-date system from online threats.
Once the D drive is encrypted, make a second copy of the recovery key today and store it somewhere away from the PC. That one step is what keeps a forgotten password from becoming lost files.
If you would rather erase the drive than lock it, you can wipe a hard drive in Windows 10.

Matt Jacobs writes and maintains the guides on Support Your Tech, which he started in 2017. He spent most of his career keeping small-business PCs running and still takes the occasional consulting job, so the steps here come from fixing the same problems on other people’s computers. Every guide is checked on his own Windows 11, Windows 10, Mac, iPhone and iPad before it goes up.