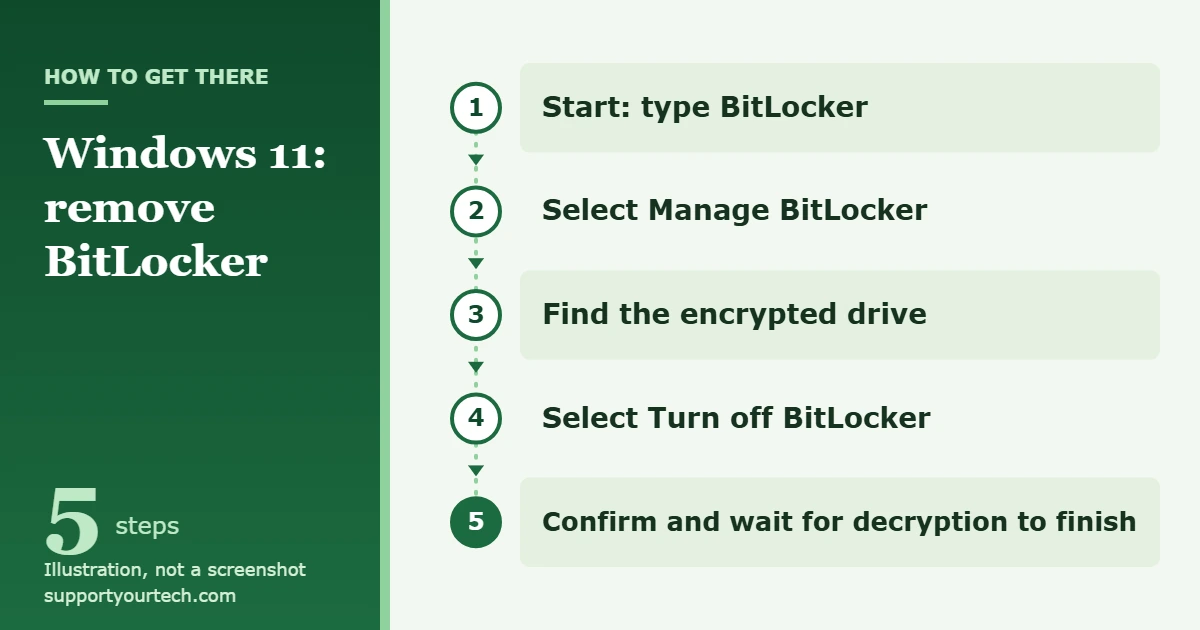
To remove BitLocker in Windows 11, open Start, type BitLocker, select Manage BitLocker, and then choose Turn off BitLocker next to the encrypted drive. Windows decrypts the drive in the background, and BitLocker is fully removed only when decryption finishes. On Windows 11 Home, the same job is done with the Device encryption switch in Settings.
Applies to: Windows 11 Pro, Enterprise and Education (BitLocker Drive Encryption) and Windows 11 Home (Device encryption). Checked against Microsoft Support and Microsoft Learn on October 6, 2026.
Before you remove BitLocker
Removing BitLocker means decrypting the drive. Your files, apps and settings stay where they are, but anyone who gets hold of the PC or the drive can then read the data without a key. Check these points first:
- Use an administrator account. Microsoft requires membership in the local Administrators group to turn BitLocker off on the Windows drive or any fixed data drive. A standard user can turn it off only on removable drives.
- Know where your recovery key is. The recovery key is a 48-digit number that unlocks the drive if Windows asks for it. For a personal PC, sign in with your Microsoft account as described in Microsoft’s guide to finding your BitLocker recovery key. A printed copy or a USB flash drive are the other common places.
- Back up important files. Decryption is designed to be safe, but a backup protects you if the drive itself fails during a long operation.
- Ask first on a work or school PC. Microsoft notes that on devices managed by an organization, encryption is usually handled by the IT department and may be required by policy.
- Unlock the drive. A locked data drive or USB drive has to be unlocked with its password or recovery key before you can turn BitLocker off.
Remove or suspend: which one do you need?
Many people who search for how to remove BitLocker only need it out of the way for a short job. Microsoft describes two different actions, and picking the right one can save hours.
| Action | What it does | Use it when |
|---|---|---|
| Turn off (decrypt) | Completely removes BitLocker protection and fully decrypts the drive. All key protectors are removed when decryption is complete. | You no longer want the drive encrypted at all. |
| Suspend | Keeps the data encrypted but stores the key unprotected on the drive, so the PC starts without checks. No decrypting or re-encrypting is needed. | You are updating the BIOS/UEFI or TPM firmware from the PC maker, or installing non-Microsoft software that changes boot components. |
You do not need either one for normal Windows updates. Microsoft states that no user action is required for BitLocker when installing Windows quality updates and feature updates.
How to remove BitLocker in Windows 11 (Pro, Enterprise, Education)
- Sign in to Windows with an administrator account.
- Select Start, type BitLocker, and select Manage BitLocker from the results. The BitLocker Drive Encryption page of Control Panel opens. You can also reach it through Control Panel > System and Security > BitLocker Drive Encryption.
- Find the drive you want to decrypt. Drives are grouped as the operating system drive, fixed data drives, and removable data drives (BitLocker To Go).
- Select Turn off BitLocker next to that drive.
- Read the message that the drive will be decrypted and that this can take some time, then confirm. Decryption starts right away.
- Keep using the PC or leave it alone while the drive decrypts. Repeat the steps for any other encrypted drive, because each drive is turned off separately.
How long this takes depends on the size, type and speed of the drive, so a large hard disk needs far longer than a small SSD. If the PC is turned off or goes into hibernation, Microsoft says decryption picks up where it stopped the next time Windows starts, even after a sudden loss of power. A laptop should still stay plugged in so the job can finish in one go.
How to turn off Device encryption on Windows 11 Home
Windows 11 Home does not include the Manage BitLocker page. Instead, it has Device encryption, a simpler feature that turns BitLocker encryption on automatically for the Windows drive and fixed drives, usually when you first sign in with a Microsoft account.
- Sign in with an administrator account.
- Open Settings and select Privacy & security > Device encryption.
- Switch the Device encryption toggle to Off and confirm if Windows asks.
- Wait while Windows decrypts the drives. You can keep working in the meantime.
One thing to know before you flip the switch: Microsoft says that once Device encryption is turned off, it will no longer turn itself on automatically. If you want protection again later, you have to switch it back on by hand in the same place.
Remove BitLocker with a command
Commands are useful when the Control Panel page will not open, when a drive is missing from it, or when you manage several PCs. Open an administrator window first: select Start, search for PowerShell, right-click Windows PowerShell, and select Run as administrator. Replace C: with the letter of the drive you want to decrypt.
PowerShell
- Type Disable-BitLocker -MountPoint “C:” and press Enter. The command removes all key protectors and begins decrypting the drive immediately.
- Type Get-BitLockerVolume -MountPoint “C:” and press Enter to check progress.
If the Windows drive holds automatic unlocking keys for other data drives, Disable-BitLocker will not proceed. Microsoft’s instruction is to run Clear-BitLockerAutoUnlock first, and then run the Disable-BitLocker command again.
manage-bde
- Type manage-bde -off C: and press Enter. This decrypts the drive and turns off BitLocker.
- Type manage-bde -status C: and press Enter to see the conversion status and percentage encrypted.
If you need to interrupt the job, manage-bde -pause C: pauses decryption and manage-bde -resume C: continues it.
How to confirm BitLocker is removed
Do not treat the drive as decrypted until Windows reports that it is. You have three ways to check:
- Control Panel: open Manage BitLocker again. A decrypted drive offers Turn on BitLocker again instead of the turn-off option.
- PowerShell: run Get-BitLockerVolume. A fully decrypted drive shows FullyDecrypted under VolumeStatus, 0 under Encryption Percentage, and Off under Protection Status.
- manage-bde: run manage-bde -status and read the conversion status, percentage encrypted and protection status lines for each drive.
To undo the change, go back to Manage BitLocker and select Turn on BitLocker, or switch the Device encryption toggle back to On on Windows 11 Home. In Manage BitLocker, Windows has you select an unlock option and back up the recovery key, then encrypts the drive again while you keep working. The full steps are in our guide on how to enable BitLocker in Windows 11.
How to suspend BitLocker instead of removing it
Suspending is the better choice before a firmware update. Microsoft warns that if protection is not suspended for that kind of update, the PC may ask for the recovery key at the next restart.
- Open Control Panel and select System and Security > BitLocker Drive Encryption.
- Select Suspend protection next to the operating system drive.
- Select Yes. Your data stays encrypted, but it is not protected until you resume.
- Do the update, then return to the same page and select Resume protection > Yes.
In an administrator PowerShell window, Suspend-BitLocker -MountPoint “C:” -RebootCount 0 suspends protection until you run Resume-BitLocker -MountPoint “C:”. RebootCount accepts values from 0 to 15 and sets how many restarts happen before protection returns on its own; if you leave it out, protection resumes after the next restart. The manage-bde equivalents are manage-bde -protectors -disable C: and manage-bde -protectors -enable C:. Microsoft documents the full procedure in Suspend BitLocker protection for non-Microsoft software updates.
Troubleshooting
Manage BitLocker does not appear in search
BitLocker Drive Encryption is available on Windows 11 Pro, Enterprise and Education. On Windows 11 Home, look for Device encryption in Settings > Privacy & security instead.
Device encryption is missing from Settings
Microsoft gives two reasons: the feature is unavailable on your device, or you are signed in with a standard user account. Sign in as an administrator and look again. If it is still missing, run manage-bde -status in an administrator window to see whether any drive is actually encrypted.
The option is greyed out or Windows says you need permission
Turning off BitLocker on the Windows drive or a fixed drive needs an administrator account. On a work or school PC, the setting may be controlled by your organization, and removing encryption without approval can break company policy. Contact your IT department.
The drive is not listed
Microsoft notes that only formatted volumes with assigned drive letters appear properly in the BitLocker Control Panel page. Use manage-bde -status to see every drive, or give the drive a letter first.
The drive is locked
Unlock it before turning BitLocker off. Use the drive’s password if it has one, or in an administrator window type manage-bde -unlock E: -recoverypassword followed by the 48-digit recovery key written exactly as shown, including the dashes. Replace E: with the drive letter.
You do not have the recovery key
If Windows starts normally and you can sign in as an administrator, you can still turn BitLocker off from inside Windows. If the PC is stuck at the recovery screen, the key is the only way in. Check your Microsoft account, your work or school account, printouts and USB drives. Microsoft Support cannot retrieve or recreate a lost key, and without it the remaining option is to reset Windows 11, which removes the data on the encrypted drive.
Frequently asked questions
Will removing BitLocker delete my files?
No. Turning off BitLocker decrypts the drive in place. Your files, apps and settings stay on the drive, just without encryption.
Can I use my PC while the drive decrypts?
Yes. Decryption runs in the background, and it continues from where it stopped if you shut down or the PC hibernates.
Do I need the recovery key to turn off BitLocker?
Not when the drive is already unlocked and you are signed in as an administrator. You need the key only if Windows is asking for it at startup or a data drive is locked. It is still wise to locate the key before you begin.
Should I remove BitLocker before a Windows update?
No. Windows quality and feature updates need no action. For BIOS/UEFI or TPM firmware updates from the PC maker, suspend protection instead of decrypting.
Will BitLocker turn itself back on?
After a full decryption it stays off until you turn it on. On PCs that use Device encryption, Microsoft says the feature no longer enables itself automatically once you have turned it off. A suspension is different: it ends on its own after the number of restarts you set, unless you chose to suspend until you resume manually.
Is the process the same in Windows 10?
The Control Panel page and commands are the same. For that version, see our guide on how to turn off BitLocker in Windows 10.
Once the status shows the drive as fully decrypted, BitLocker is removed. If the PC ever leaves your home or holds private files, plan to turn encryption back on when your task is done, and save the new recovery key somewhere other than the PC itself.
Matt Jacobs has been working as an IT consultant for small businesses since receiving his Master’s degree in 2003. While he still does some consulting work, his primary focus now is on creating technology support content for SupportYourTech.com.
His work can be found on many websites and focuses on topics such as Microsoft Office, Apple devices, Android devices, Photoshop, and more.